The Banking App That Passed the Demo but Failed the Audit
An Indian NBFC builds a custom lending application. The demo is smooth: instant KYC, automated underwriting, disbursement in minutes. The board approves. The app launches.
Six months later, an RBI inspection raises three questions. First, the underwriting model was never independently validated—it was built by the same team that owns it. Second, the AI-driven credit decisions have no documented human oversight mechanism, and customers cannot request a human review. Third, the consent records for data sharing with a third-party analytics vendor cannot be produced in a form that shows what the customer agreed to, when, and through which channel.
The app worked. The governance did not. And in banking, governance is not optional.
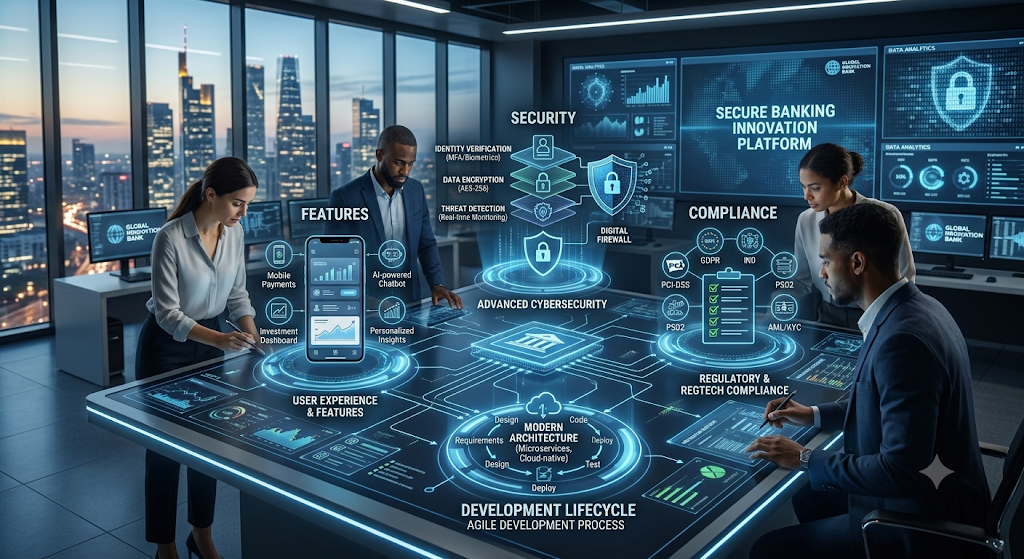
This is the defining tension in custom banking software development. Unlike fintech products built for speed, banking software operates inside a regulatory perimeter where the RBI mandates model risk management, the DPDPA mandates consent traceability, and the Board is ultimately accountable for every outsourced system. The software must be built not just to function, but to be auditable, explainable, and governable.
The regulatory framework tightened significantly in 2026. RBI released draft Guidance on Regulatory Principles for Model Risk Management in June 2026, requiring Board-approved frameworks, independent validation of all models (including third-party and AI/ML systems), model inventories, and human oversight with kill-switch mechanisms for AI-driven decisions . The DPDPA Rules are phasing in: Consent Manager requirements take effect from 13 November 2026, with wider obligations covering notice, consent, security, and breach reporting following on 13 May 2027 . And RBI's outsourcing directions require banks to ensure service providers meet business continuity and incident reporting timelines—including reporting cyber incidents fast enough for the bank to notify RBI within six hours .
This guide is written for Indian banks, NBFCs, and financial institution technology leaders evaluating custom banking software. We will cover the core features, the zero-trust security architecture, the RBI AI governance requirements, the DPDPA consent infrastructure, real costs in rupees and dollars, and a phased implementation framework with clear go/no-go gates.
Core Features: What Custom Banking Software Must Include
Custom banking software is not a single application. It is a set of interconnected modules serving retail, corporate, and internal users. The must-have features in 2026 reflect both customer expectations and regulatory requirements.
The Customer-Facing Modules
1. Omnichannel access. Mobile, web, branch, and API channels serving a consistent view of the customer. RBI's model risk guidance and the broader digital banking trend point toward unified customer views across channels .
2. Automated onboarding and KYC. Aadhaar-based eKYC, PAN verification, video KYC, and document verification with audit trails. The onboarding flow must capture consent for each purpose separately .
3. Real-time payments. UPI, IMPS, NEFT, RTGS, and card payments with real-time status. Multi-currency support for trade finance and NRI banking .
4. AI-driven personalisation and decisioning. Product recommendations, spending insights, and credit decisions. Every AI-driven decision must have human oversight and explainability .
5. Embedded finance and API integrations. Open banking APIs for third-party integrations, account aggregator connectivity, and partner ecosystems .
The Core Banking Modules
6. Deposits and loans. Account management, interest calculation, loan origination, servicing, and collections. These are the core modules that define a core banking system .
7. General ledger and accounting. Double-entry ledger, reconciliation, and financial reporting. The ledger must be atomic and auditable.
8. Enterprise customer solutions. Corporate banking, trade finance, cash management, and treasury .
The Internal and Governance Modules
9. Model inventory and risk management. A registry of every model in use—including AI/ML models, third-party models, and spreadsheet-based tools that materially influence decisions—with risk tiering, validation records, and approval status .
10. Consent management. Purpose-specific consent capture, storage, and withdrawal across channels, with audit trails .
11. Audit and explainability. Decision logs showing what data was used, what model produced the output, and what human review occurred. Required for both RBI and DPDPA accountability.
12. Business continuity and incident reporting. The software must support incident detection, reporting timelines, and recovery objectives that meet RBI's outsourcing and continuity requirements .
The Feature Priority Table
| Category | Module | Regulatory Driver |
|---|---|---|
| Customer | Omnichannel, KYC, payments, AI personalisation | RBI digital banking, DPDPA consent |
| Core | Deposits, loans, ledger, enterprise solutions | Core banking functional requirements |
| Governance | Model inventory, consent, audit, BCP | RBI Model Risk, DPDPA, Outsourcing Directions |
For teams building the secure integrations and AI governance layers, our Custom Software Development and AI Consulting practices cover the full stack.
Security Architecture: Zero Trust and Beyond
Banking security is not a perimeter defence. It is a layered architecture where every request is verified, every action is logged, and every failure is contained.
The Zero-Trust Foundation
Zero trust means no implicit trust based on network location. Every request—from a branch terminal, a mobile app, or an internal service—is authenticated, authorised, and encrypted.
The components:
Identity and access management. Multi-factor authentication, biometric authentication, role-based access control, and privileged access management .
Service-to-service authentication. Mutual TLS between microservices. No service trusts another by default.
Secrets management. Hardware Security Modules (HSM) or cloud HSM for key storage. AES-256 encryption for data at rest .
API security. Rate limiting, input validation, and OWASP-compliant development practices .
Data Protection
Encryption in transit and at rest. TLS for all communication; AES-256 for stored data.
Data masking. Sensitive fields masked in non-production environments and for users who do not need full visibility.
Data Loss Prevention (DLP). Monitoring and restricting unauthorised internal movement of sensitive data. Some Indian banks have issued procurement requests for DLP solutions .
Immutable audit trails. Logs that cannot be altered, for forensic and regulatory review.
Application Security
Secure development lifecycle. Threat modelling, code review, and dependency scanning.
Vulnerability assessment and penetration testing. Regular VA/PT by independent auditors .
OWASP compliance. Protection against injection, broken authentication, and other common vulnerabilities .
Runtime protection. Web application firewalls and runtime application self-protection for critical services.
The Security Standards
Custom banking software must align with multiple standards:
PCI DSS for payment card data .
ISO 27001 for information security management .
SOC 2 for service organisation controls .
Basel III for banking supervision and risk management .
RBI Cyber Security Framework for regulated entities .
The Security Architecture Table
| Layer | Control | Standard |
|---|---|---|
| Identity | MFA, biometrics, RBAC | RBI, PCI DSS |
| Data | AES-256, TLS, DLP | ISO 27001, DPDPA |
| Application | OWASP, SAST/DAST, WAF | PCI DSS |
| Operations | VA/PT, incident response | RBI Cyber Security |
RBI's AI Governance Framework: What Banking Software Must Support RBI's draft Model Risk Management guidance (June 2026) is the most significant regulatory development for banking AI. It applies to banks, NBFCs, and other regulated entities, and it has direct implications for how custom banking software is built.
The Model Inventory
Every model used in decision-making must be in a comprehensive inventory, including active, inactive, and decommissioned models. No model can be used unless it is in the inventory. The inventory must capture model owners, developers, validators, approvers, risk tiers, and validation observations .
Software implication: The banking platform must include a model registry—not as a spreadsheet, but as a governed system with access control, versioning, and audit trails.
Independent Validation
All models, including third-party and vendor models, must be independently validated. The entity remains accountable for third-party model outcomes, and cannot rely solely on vendor certification .
Software implication: The platform must support validation workflows: a separate validation team with its own access, validation records attached to the model, and a gate that prevents deployment without validation sign-off.
Human Oversight and Kill Switch
AI-driven decisions must have human oversight. For customer-facing AI, the entity must disclose AI usage and provide an option to switch to human assistance. The guidance also proposes kill-switch mechanisms to halt AI systems .
Software implication: The platform must implement human-in-the-loop workflows for consequential decisions, a customer-facing AI disclosure, a human escalation path, and an operational kill switch that can disable an AI model without disabling the entire application.
Risk Tiering and Board Approval
Models must be classified by risk (materiality, complexity, supervisory considerations). High-risk models require approval from the Risk Management Committee of the Board; lower-risk models may use delegated approval .
Software implication: The model registry must support risk tier assignment, approval workflows that route to the correct authority, and evidence that Board-level approval was obtained for high-risk models.
The AI Governance Table
| Requirement | Software Capability |
|---|---|
| Model inventory | Model registry with lifecycle states |
| Independent validation | Validation workflow, access separation |
| Human oversight | HITL workflows, escalation paths |
| Kill switch | Model-level disable control |
| Risk tiering | Classification and approval routing |
| Third-party models | Vendor due diligence records |
DPDPA Consent Infrastructure: The 2026 Deadline
The DPDPA Rules impose consent obligations that banking software must support. The Consent Manager requirements take effect from 13 November 2026, with wider obligations from 13 May 2027 .
The Consent Challenge in Banking
Banking involves multiple purposes for the same customer: account operation, KYC, credit assessment, marketing, third-party sharing, and analytics. Under the DPDPA, consent must be specific, informed, and traceable to what the customer saw, when, and through which channel .
The practical problem: Many banks cannot currently state how many versions of a customer's data exist across operational and analytical systems, or which system is authoritative when a customer exercises access, correction, or erasure rights .
What the Software Must Support
1. Purpose-specific consent capture. At onboarding and at each new purpose, the customer grants consent separately. A bundled consent is not valid.
2. Cross-channel consent records. Consent granted at a branch, on the mobile app, through a DSA, or on a call must be captured and linked to the same customer identity.
3. Consent withdrawal propagation. When a customer withdraws consent for a purpose, the system must stop processing for that purpose—across CRM, marketing tools, and analytics—while retaining data required by law (PMLA, KYC, credit reporting) .
4. Audit trails. Evidence of what notice was shown, when, and what action the customer took .
5. Data discovery and mapping. The ability to locate personal data across systems for access and erasure requests.
The Consent Management Table
| Capability | Requirement | Deadline |
|---|---|---|
| Purpose-specific capture | DPDPA Section 6 | Nov 2026 |
| Cross-channel records | Traceability | Nov 2026 |
| Withdrawal propagation | Erasure/purpose limitation | May 2027 |
| Audit trails | Evidence of consent | Nov 2026 |
| Data mapping | Access/erasure fulfillment | May 2027 |
Real Costs in India (2026)
Custom banking software costs are driven by the regulatory scope, the number of modules, the integration complexity, and the validation and audit requirements.
Build Costs
| Scope | Build Cost (₹) | Build Cost ($ approx.) | Timeline |
|---|---|---|---|
| Digital lending MVP (KYC, underwriting, disbursement) | ₹30–70 lakh | $36,000–$84,000 | 20–32 weeks |
| Retail banking module (accounts, payments, mobile) | ₹50 lakh–₹1.5 crore | $60,000–$1,80,000 | 28–40 weeks |
| Core banking platform (deposits, loans, ledger, enterprise) | ₹1.5–5 crore+ | $1,80,000–$6,00,000+ | 40–60+ weeks |
| AI governance layer (model registry, validation workflow, HITL) | ₹20–60 lakh | $24,000–$72,000 | 16–28 weeks |
| DPDPA consent platform | ₹15–40 lakh | $18,000–$48,000 | 12–20 weeks |
Note: USD conversions at ₹83/$. Ranges are indicative for Indian banks and NBFCs. Regulatory licensing, third-party integrations, and ongoing validation audits are additional.
Running Costs
| Component | Monthly Range (₹) | Monthly Range ($ approx.) | Notes |
|---|---|---|---|
| Infrastructure | ₹50,000–₹5,00,000 | $600–$6,000 | Indian data centres |
| Security monitoring | ₹30,000–₹1,50,000 | $360–$1,800 | SIEM, SOC |
| Model validation | ₹20,000–₹1,00,000 | $240–$1,200 | Ongoing validation |
| Compliance and audit | ₹50,000–₹2,00,000 | $600–$2,400 | VA/PT, audits |
The Regulatory Cost
The regulatory requirements add cost that fintech products do not bear: independent model validation, Board-level governance, audit trails, and business continuity testing. These are not optional. Budget 20–30% of the total programme for governance and compliance.
Implementation Framework: A Phased Approach With Cost Gates
Phase 1: Regulatory Scoping and Architecture (Week 1–4)
Objective: Map the regulatory requirements and design the governance architecture.
Activities:
Identify the regulatory category (bank, NBFC, payment system).
Map RBI Model Risk, DPDPA, and outsourcing requirements.
Design the model registry and consent architecture.
Define the security architecture (zero trust).
Assess existing systems and integration points.
Cost: ₹2–8 lakh ($2,400–$9,600).
Go/No-Go: Regulatory scope documented. Architecture approved.
Phase 2: Core Build with Governance Hooks (Week 5–20)
Objective: Build the core modules with governance built in.
Activities:
Build the core modules (accounts, payments, or lending).
Implement zero-trust security.
Build the model registry and validation workflow.
Build the consent capture and withdrawal workflow.
Implement audit logging.
Cost: ₹50 lakh–₹1.5 crore ($60,000–$1,80,000).
Go/No-Go: Core works. Governance hooks functional.
Phase 3: AI and Model Integration (Week 21–32)
Objective: Integrate AI models with the governance layer.
Activities:
Integrate credit scoring, fraud detection, or personalisation models.
Register models in the inventory.
Implement independent validation workflow.
Implement human-in-the-loop for consequential decisions.
Implement AI disclosure and kill switch.
Cost: ₹20–60 lakh ($24,000–$72,000).
Go/No-Go: Models registered and validated. HITL works.
Phase 4: Security and Compliance Testing (Week 33–40)
Objective: Validate security and compliance.
Activities:
Penetration testing and VA.
DPDPA consent audit.
Model risk governance review.
Business continuity testing.
Incident reporting drill.
Cost: ₹5–20 lakh ($6,000–$24,000).
Go/No-Go: Tests pass. Compliance review passes.
Phase 5: Pilot and Scale (Month 10–12)
Objective: Pilot and scale.
Activities:
Pilot with a limited customer cohort.
Monitor model performance and consent compliance.
Scale to full production.
Establish ongoing validation and audit cadence.
Cost: Running costs plus governance.
Go/No-Go: Pilot meets regulatory and operational criteria.
Phase Summary Table
| Phase | Duration | Key Deliverable | Cost (₹) | Go/No-Go Criteria |
|---|---|---|---|---|
| 1. Scoping | 4 weeks | Regulatory map, architecture | 2–8 lakh | Approved |
| 2. Core Build | 16 weeks | Core modules, governance hooks | 50 lakh–1.5 crore | Works |
| 3. AI Integration | 12 weeks | Models, HITL, kill switch | 20–60 lakh | Validated |
| 4. Testing | 8 weeks | Security, compliance, BCP | 5–20 lakh | Passes |
| 5. Pilot | 12 weeks | Production pilot | Running costs | Meets criteria |
Risks, Pitfalls, and Governance
The Most Common Custom Banking Software Failures
Governance retrofitted. The AI model is built and deployed, then the governance layer is added. Retrofitting is expensive and may require re-architecture. Mitigation: Build governance hooks in phase one.
Consent bundled. The onboarding form captures a single "I agree" for all purposes. This fails DPDPA specificity. Mitigation: Purpose-specific consent from day one.
Model inventory in spreadsheets. The model registry is a spreadsheet maintained by one person. It becomes stale and unauditable. Mitigation: Governed model registry system.
No human oversight for AI decisions. Credit decisions are fully automated with no escalation path. Mitigation: HITL workflows for consequential decisions.
Third-party model accountability gap. The vendor says their model is validated; the bank relies on that. RBI requires independent validation. Mitigation: Independent validation of all models.
Incident reporting too slow. The vendor's incident process promises 24-hour notice; RBI requires six-hour reporting. Mitigation: Contractual incident reporting SLAs that meet RBI timelines.
Risk Summary Table
| Risk | Likelihood | Impact | Mitigation |
|---|---|---|---|
| Governance retrofitted | High | High (rework) | Build hooks early |
| Bundled consent | High | High (DPDPA) | Purpose-specific |
| Spreadsheet registry | High | Medium (audit) | Governed system |
| No HITL | High | High (RBI) | Escalation paths |
| Third-party model gap | Medium | High | Independent validation |
| Slow incident reporting | Medium | High (RBI) | Contract SLAs |
Benchmark Summary and Decision Framework
Decision Matrix: Build vs Extend vs Buy
| Your Situation | Recommended Path |
|---|---|
| Unique workflow, regulated entity | Build custom with governance |
| Standard core, limited differentiation | Extend a core banking platform |
| NBFC lending, no core banking licence | Build custom lending platform |
| Small co-operative bank | Buy a plug-and-play core module |
Governance Priority Table
| Priority | Capability | Why |
|---|---|---|
| 1 | Model registry | RBI inventory requirement |
| 2 | Purpose-specific consent | DPDPA November 2026 |
| 3 | Independent validation | RBI Model Risk |
| 4 | Human oversight | RBI AI governance |
| 5 | Audit and explainability | Accountability |
The One-Paragraph Decision Rule
If you are building custom banking software, start with the governance layer, not the features. Build the model registry, the consent capture, and the audit trail before you build the AI. Ensure every AI-driven decision has human oversight and a kill switch. Ensure every consent is purpose-specific and traceable. And ensure your incident reporting can meet RBI's six-hour timeline. The features can be iterated. The governance cannot be retrofitted.
Frequently Asked Questions
1. How much does custom banking software development cost in India?
A digital lending MVP costs ₹30–70 lakh ($36,000–$84,000). A retail banking module costs ₹50 lakh–₹1.5 crore. A core banking platform costs ₹1.5–5 crore+. Governance layers add ₹35–100 lakh.
2. What is RBI's Model Risk Management guidance?
Draft guidance released in June 2026 requiring Board-approved frameworks, independent validation of all models (including third-party and AI/ML), model inventories, risk tiering, and human oversight with kill switches for AI decisions .
3. What are the DPDPA deadlines for banking software?
Consent Manager requirements take effect from 13 November 2026. Wider obligations covering notice, consent, security, and breach reporting follow on 13 May 2027 .
4. How must banking software handle AI-driven decisions?
AI-driven decisions must have human oversight, a customer-facing disclosure that AI is being used, an option for the customer to switch to human assistance, and a kill-switch mechanism .
5. What are the security standards for custom banking software?
PCI DSS, ISO 27001, SOC 2, Basel III, and RBI's Cyber Security Framework. Zero-trust architecture, AES-256 encryption, HSMs, and OWASP-compliant development .
6. How does RBI's outsourcing guidance affect custom software?
The bank remains accountable for outsourced services. Service providers must meet business continuity and incident reporting timelines—including reporting cyber incidents fast enough for the bank to notify RBI within six hours .
7. What is a model inventory and why is it required?
A comprehensive registry of all models (active, inactive, decommissioned) used in decision-making, with owners, risk tiers, and validation records. RBI requires it, and no model can be used unless it is in the inventory .
8. How should consent be captured in banking software?
Consent must be free, specific, informed, and unambiguous. It must be captured per purpose, traceable to what the customer saw and when, and withdrawal must propagate across systems while retaining legally required data .
9. What is the biggest risk in custom banking software?
Building governance after the features. The model registry, consent infrastructure, and audit trails must be designed in from the start.
10. Should a bank build or buy core banking software?
Build if you have unique workflows and the engineering capability to meet regulatory requirements. Buy or extend a platform if you have standard needs and limited engineering.
11. How long does custom banking software take?
A lending MVP takes 20–32 weeks. A retail banking module takes 28–40 weeks. A core banking platform takes 40–60+ weeks. Timeline depends on scope and regulatory requirements.
12. How can Innovative AI Solutions help?
Innovative AI Solutions builds custom banking software for Indian banks and NBFCs—core modules, zero-trust security, model registries, human-in-the-loop workflows, DPDPA consent platforms, and RBI-compliant governance. Our Delhi-based team handles regulatory scoping, architecture, implementation, and validation. Visit https://innovativeais.com to discuss your requirements.
Contact Innovative AI Solutions
Ready to build banking software that passes the audit, not just the demo?
[One-line supporting sentence.]
Contact Information
Innovative AI Solutions
📍 Netaji Subhash Place, Pitampura, Delhi – 110034
🌐 Website: https://innovativeaislabs.com 📧 Email: info@innovativeais.com
📞 Phone: +91 7464 099 059 / +91 96899 67356
Business Services
AI Automation
AI Development
AI Consulting
Machine Learning Solutions
Deep Learning Solutions
Generative AI Services
NLP Solutions
AI Agents
AI Chatbots
Voice AI
CRM Development
Custom Software Development
Website Development
Mobile App Development
About the Author
Abhishek Kumar
Founder & CEO, Innovative AI Solutions
5+ years building production AI systems for Indian businesses. Based in Delhi, serving clients across India.
Ready to build AI solutions for your business?
Innovative AI Solutions — Delhi's leading AI development company. Free consultation available.
Get Free Consultation →
A practical 2026 guide for Indian banks and NBFCs building custom banking software—core features, zero-trust security, RBI model risk governance, DPDPA consent infrastructure, real rupee costs, and a phased implementation that treats governance as architecture.
#CustomBankingSoftware #BankingSoftwareDevelopment #CoreBanking #RBIAIGovernance #ModelRiskManagement #DPDPA #ZeroTrust #BankingSecurity #DigitalBanking #NBFCTechnology #IndiaBanking #DelhiNCR #InnovativeAISolutions
Copyright ©️ 2015–2026 Innovative AI Solutions. All Rights Reserved. | Privacy Policy | Terms & Conditions